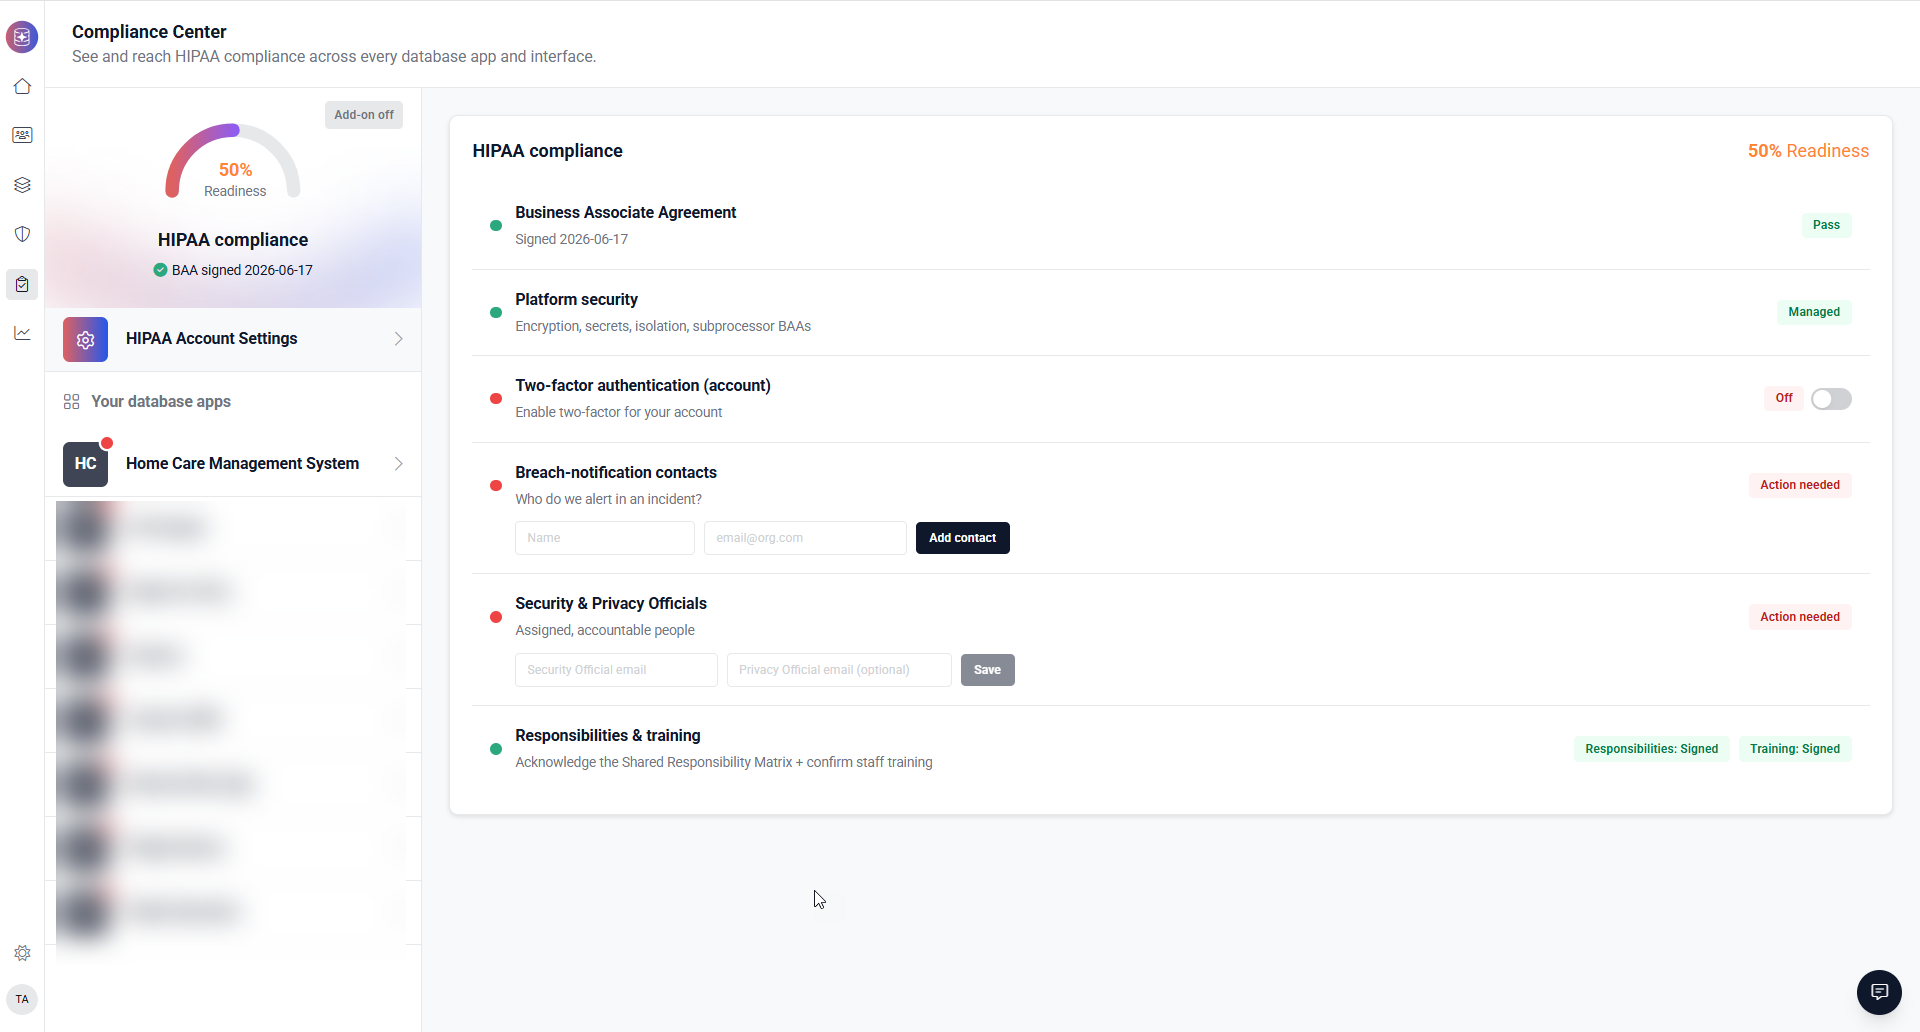
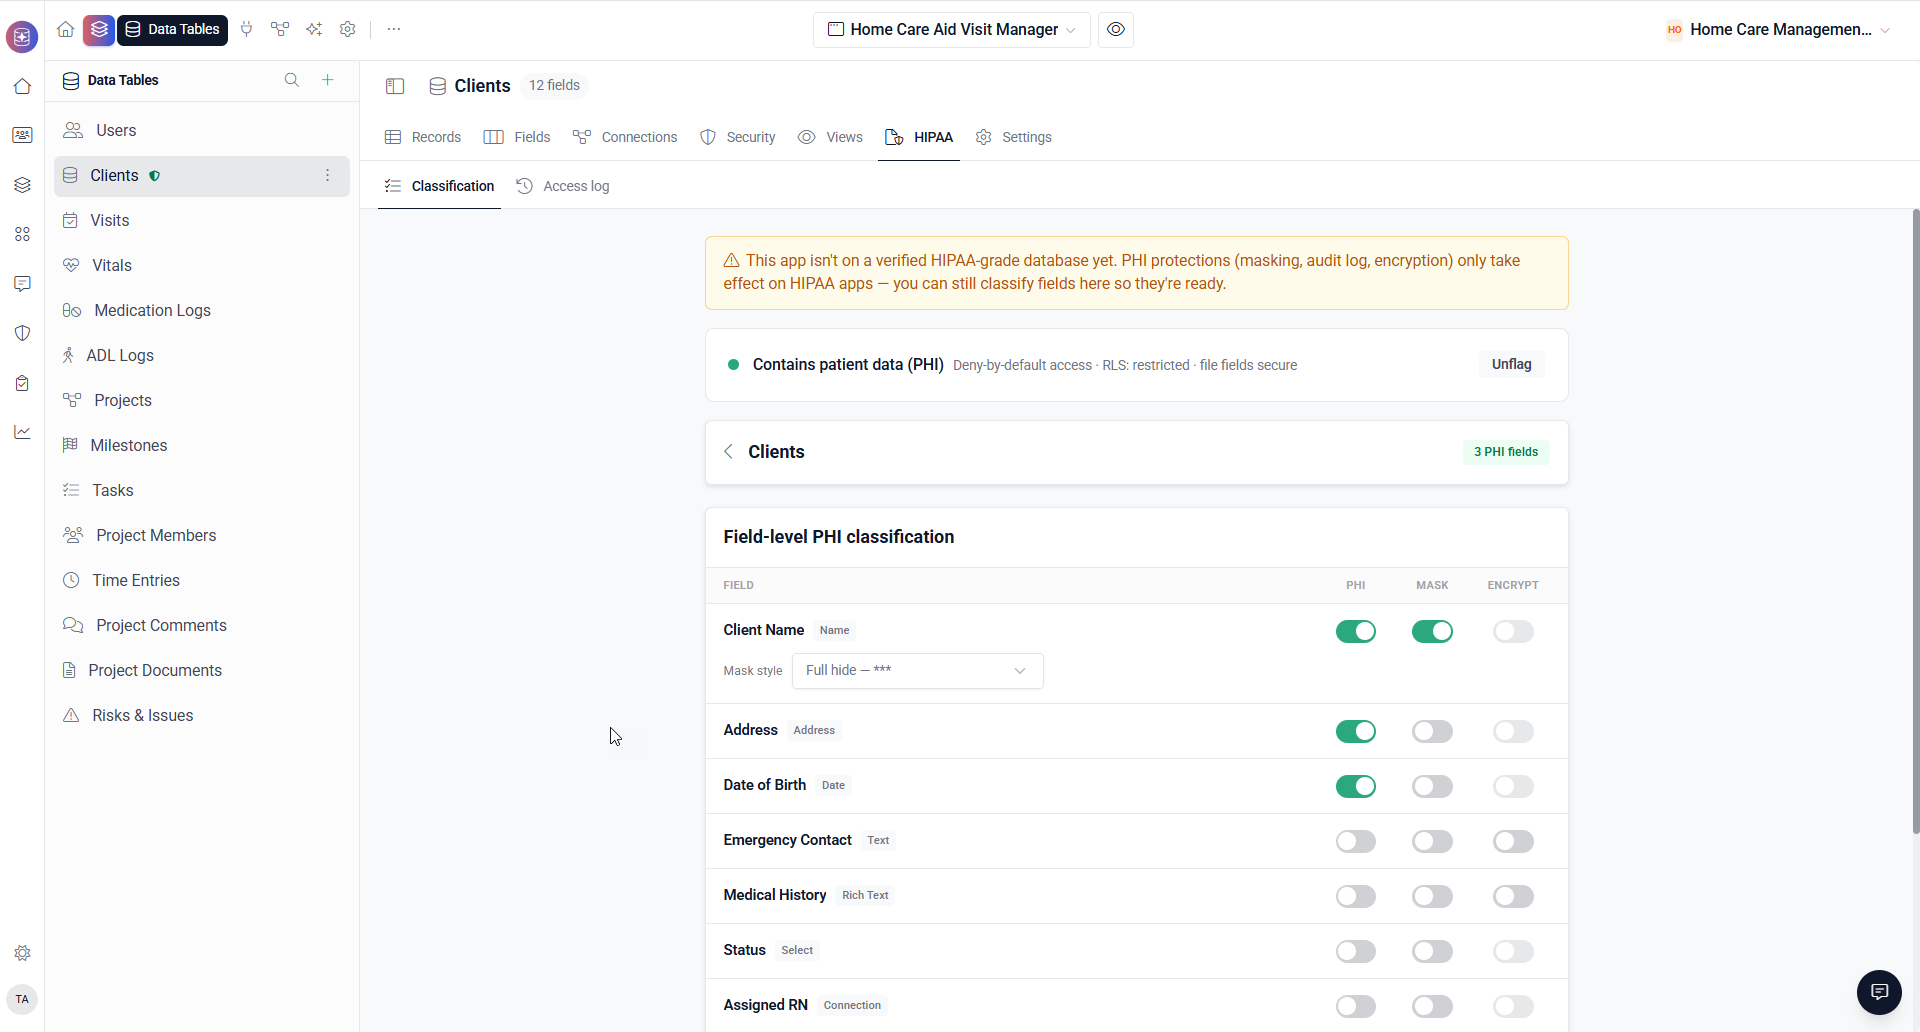
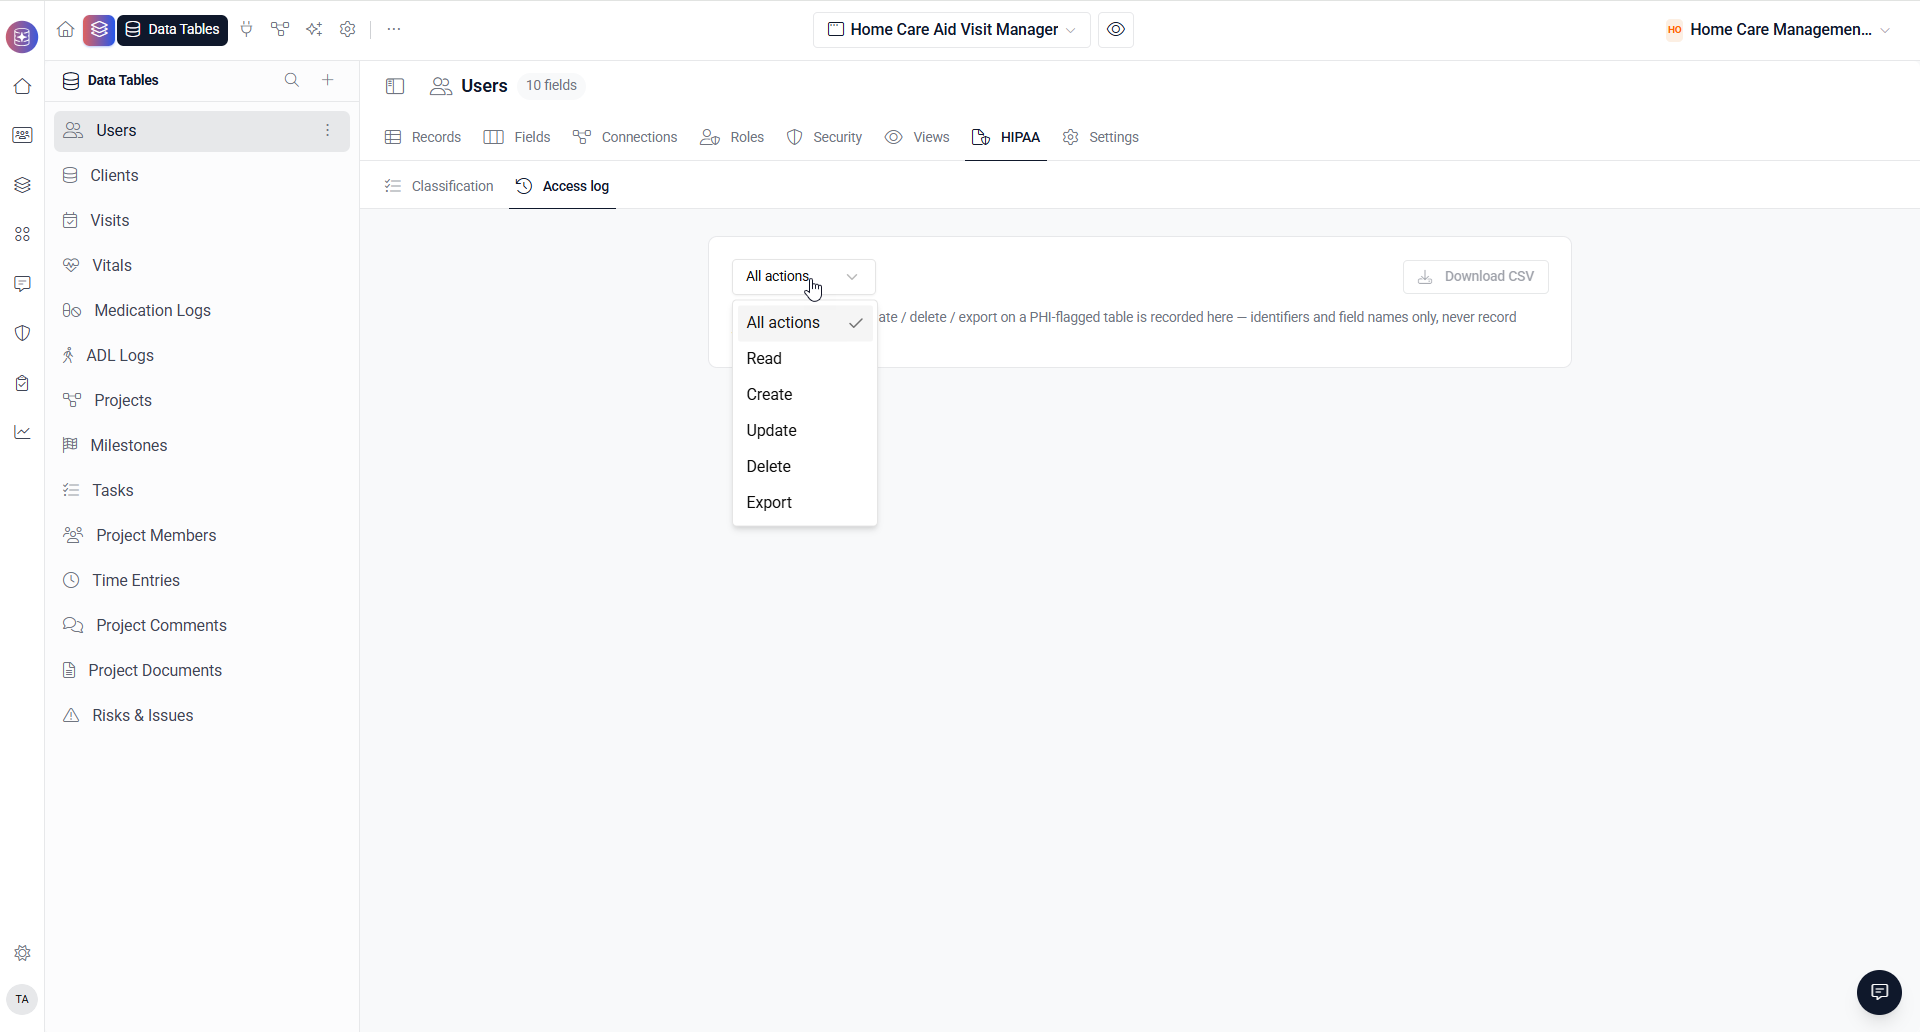
Looking for some community’s insight here, since TB itself does not have any reliable workaround to offer.
Context
My app handle sensitive personal data, the same level of sensitivity that an hospital handles medical patients information.
Issue
Currently, there is no way to tell who access which page/records to trigger alerts or at least have an access log to track and know who saw information without authorization. This cause a major potential data breach issue, and we have no way of knowing that and who is at fault.
Solution?
Since TB is HIPAA graded, I would assume there’s some basic security features for that, but apparently not. So how do you manage that situation with personal data at stake? Did you created some custom features?
Thanks for taking the time to respond to this issue. The feature you are describing seems to really address the need yes! I would love to see it more in depth.
After, the big question is: will it be pushed in all plans ?
Hi Manuel — Greg here from the Tadabase team, jumping in for Moe.
Honest answer on “all plans”: final packaging isn’t locked yet, so I won’t pretend it is. The way it’s shaping up, the compliance center and PHI tagging sit with our compliance capabilities (the same family as HIPAA/BAA today) rather than in every plan. Granular access-audit tooling is the kind of thing regulated apps rely on, and we’d rather build it properly for that use case than water it down to check a box everywhere.
What exists today on your current plan: activity is captured in the page logs, so there is a record — it’s just not the “who viewed this specific record” view you’re after. The new tooling is exactly that view.
Want to see it in depth? Email me at greg@tadabase.io and I’ll set up a time with Akiva, our head of AI, to walk you through it. If you mention roughly how many users touch the sensitive records and whether you’re under a specific framework (HIPAA, Law 25 / Quebec, GDPR), we’ll make the walkthrough match your actual setup.